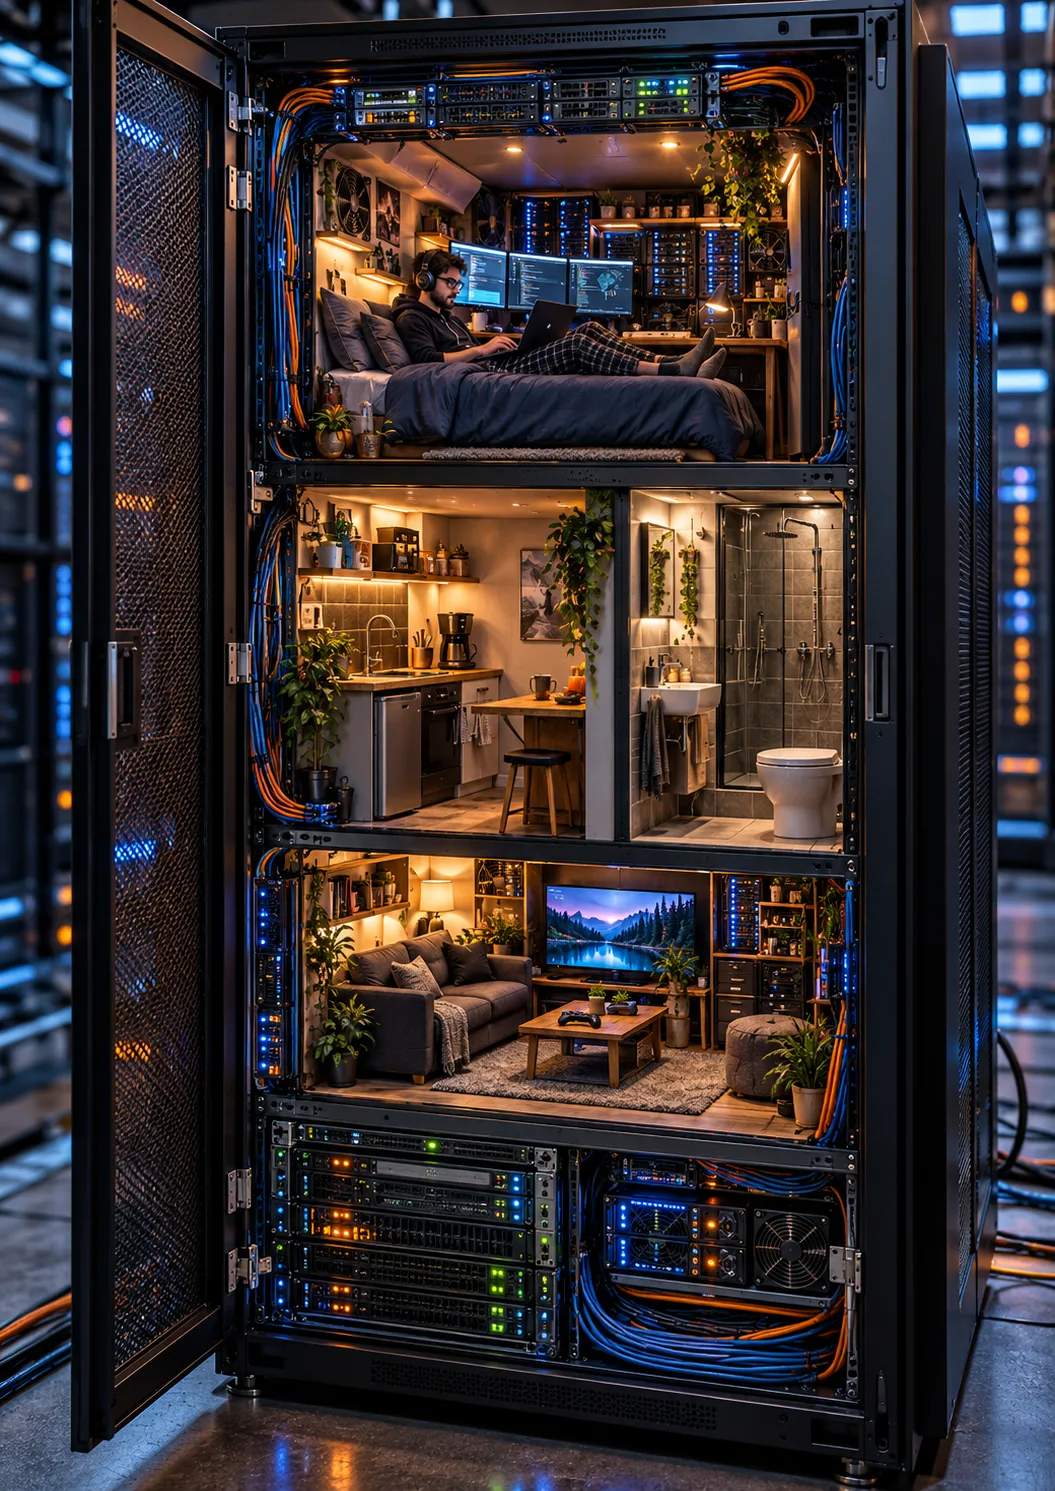
Yesterday, I spent the whole day in a kickoff meeting with one of the state agencies.
What started as a conventional 系统 project has now moved in a very different direction.
Instead of simply delivering software, the 系统 will have a 实时 AI agent embedded inside it, operating within defined 工作流, permissions, guardrails and kill-switch controls.
The most interesting part is the level of acceptance.
In the past, getting VM access inside certain organisations - even for a small, isolated application - could be extremely difficult.
今天, some are already open to allowing a 实时 AI agent to operate with sudoer privileges, and in tightly controlled cases, even full root access inside an isolated VM.
That is a significant shift.
It shows that the conversation is moving beyond whether AI is capable enough. The real questions are now about trust, control, security and how safely AI can operate inside real organisational infrastructure.
Once that trust is established, AI stops being just another application.
It becomes part of the operating layer.
Ultimately, our vision is to inject our own AI 智能体 and LLM intelligence layer into every client 系统, turning each deployment into an adaptive asset that grows in capability and value over time.
#AgentAI #AI基础设施 #企业版AI #AI自动化 #LLM #DigitalTransformation #AI工程

Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
这篇文章把getting VM access inside certain讲得比一般的AI介绍更具体。
如果可以继续说明guardrails and kill-switch controls的真实案例,我会想继续阅读。
这个主题读起来很清楚,也容易跟着理解。