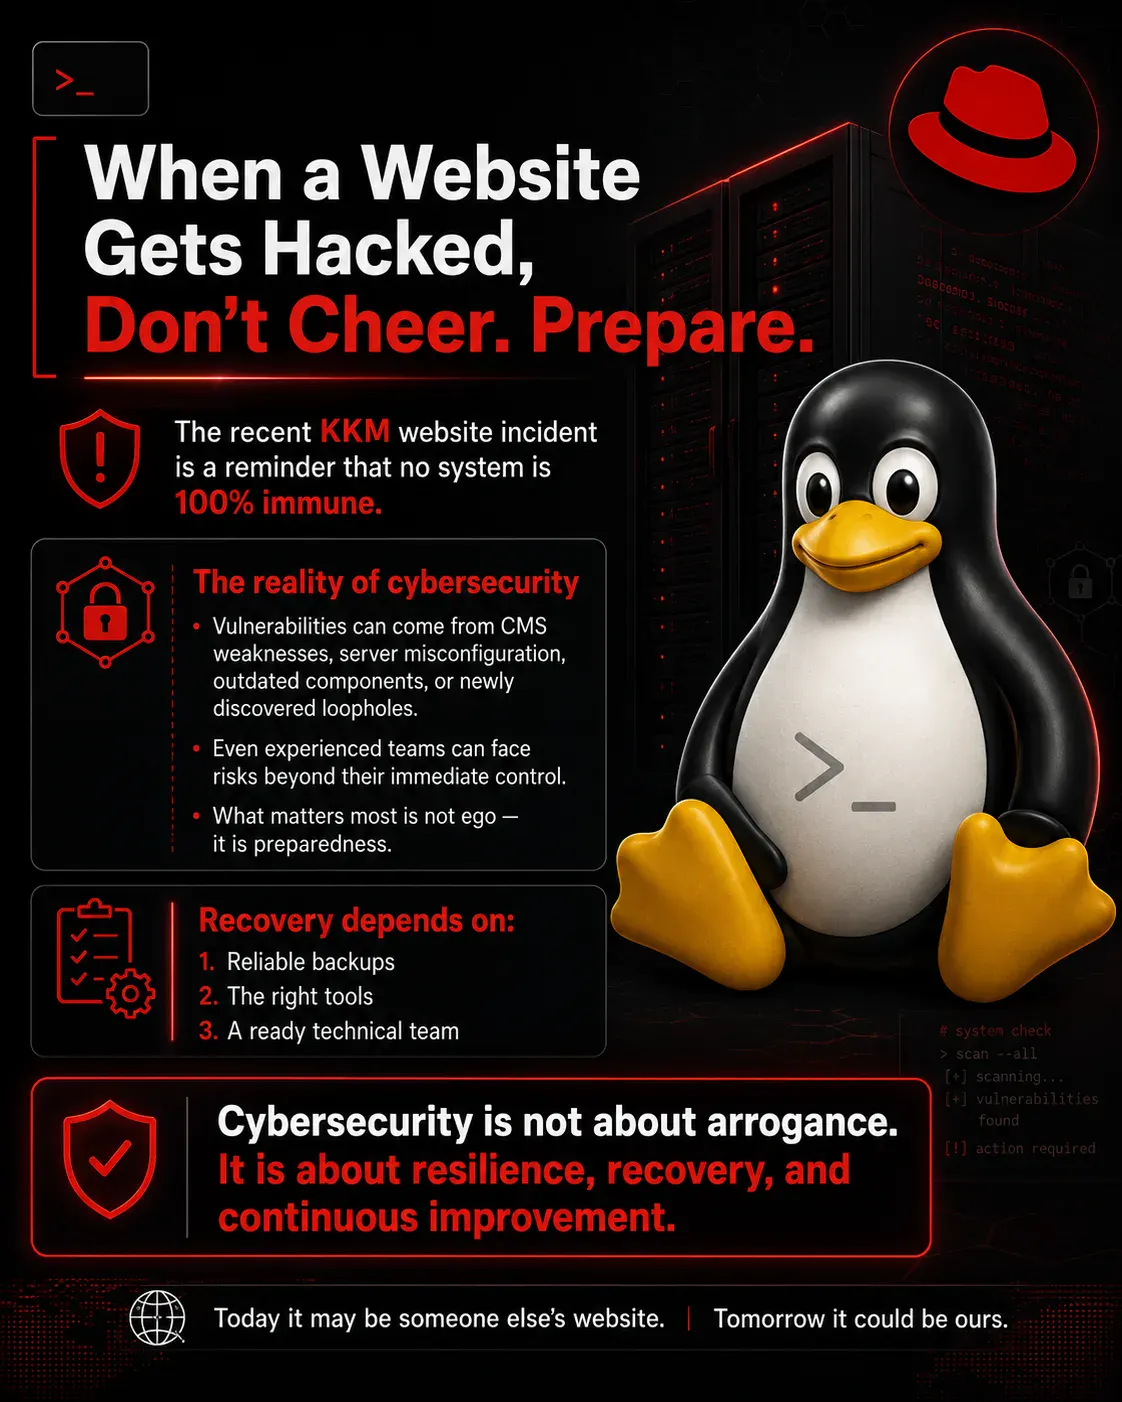
从 an engineering and integration standpoint, reports that the KKM website was hacked or defaced are a useful field reminder: in production 系统, security is not a place for ego.
Whenever a high-profile site goes down, the public response is usually criticism. 安全 consultants, AI engineers, and tech commentators often talk as if their own stacks are somehow exempt from the same failure modes.
The field reality is different.
No 实时 系统 is 100% safe. 政府 portals, corporate platforms, 中小企业 站点, CMS instances, and even hardened servers can still take a hit. Attack paths are real: stale CMS versions, vulnerable plugins, misconfigured servers, weak access controls, patch lag, or zero-day gaps that were not known at the last review.
Sometimes the issue is not whether the team is competent. It is whether the organization has rehearsed what happens when a layer fails.
This is why backups, monitoring, scheduled audits, server hardening, incident-response playbooks, and recovery drills matter in production.
A defaced site is not only a technical outage. It is a business-continuity event, a trust hit, and a reputational signal.
Mean time to recovery hinges on three operational factors:
- 备份 integrity and coverage
- Tooling and automation on hand
- 团队 readiness under pressure
安全 work should not be about pointing at another team's outage. It should be about learning from it and tightening your own stack before you face the same failure.
今天, it is someone else's production surface.
Tomorrow, it could be ours.
良好 security is not about being the loudest voice in the room. It is about being prepared, disciplined, and continuously improving.
#Cyber安全 #网站安全 #商业Continuity #DigitalRisk #事件响应 #中小企业 #科技 #NeuralOps


Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
这个主题这部分我看了几遍,值得再想。
我们团队正好在讨论这篇文章,这篇来得及时。
文章对reports that the KKM website的结论比较平衡,不只是强调好处。
这篇文章适合团队用来开始讨论sometimes the issue。
文章把mean time to recovery hinges和日常运营联系起来,这一点很有帮助。
我会把whenever a high-profile site goes这一段分享给需要了解技术的同事。
收藏了,主要是为了从 an engineering and integration。
我特别喜欢备份 integrity and coverage tooling这一部分,内容没有把实施过程说得太简单。