Yesterday I spent the whole day in a kickoff meeting with one of the state agencies.
What started as a conventional 系统 project has since moved in a very different direction.
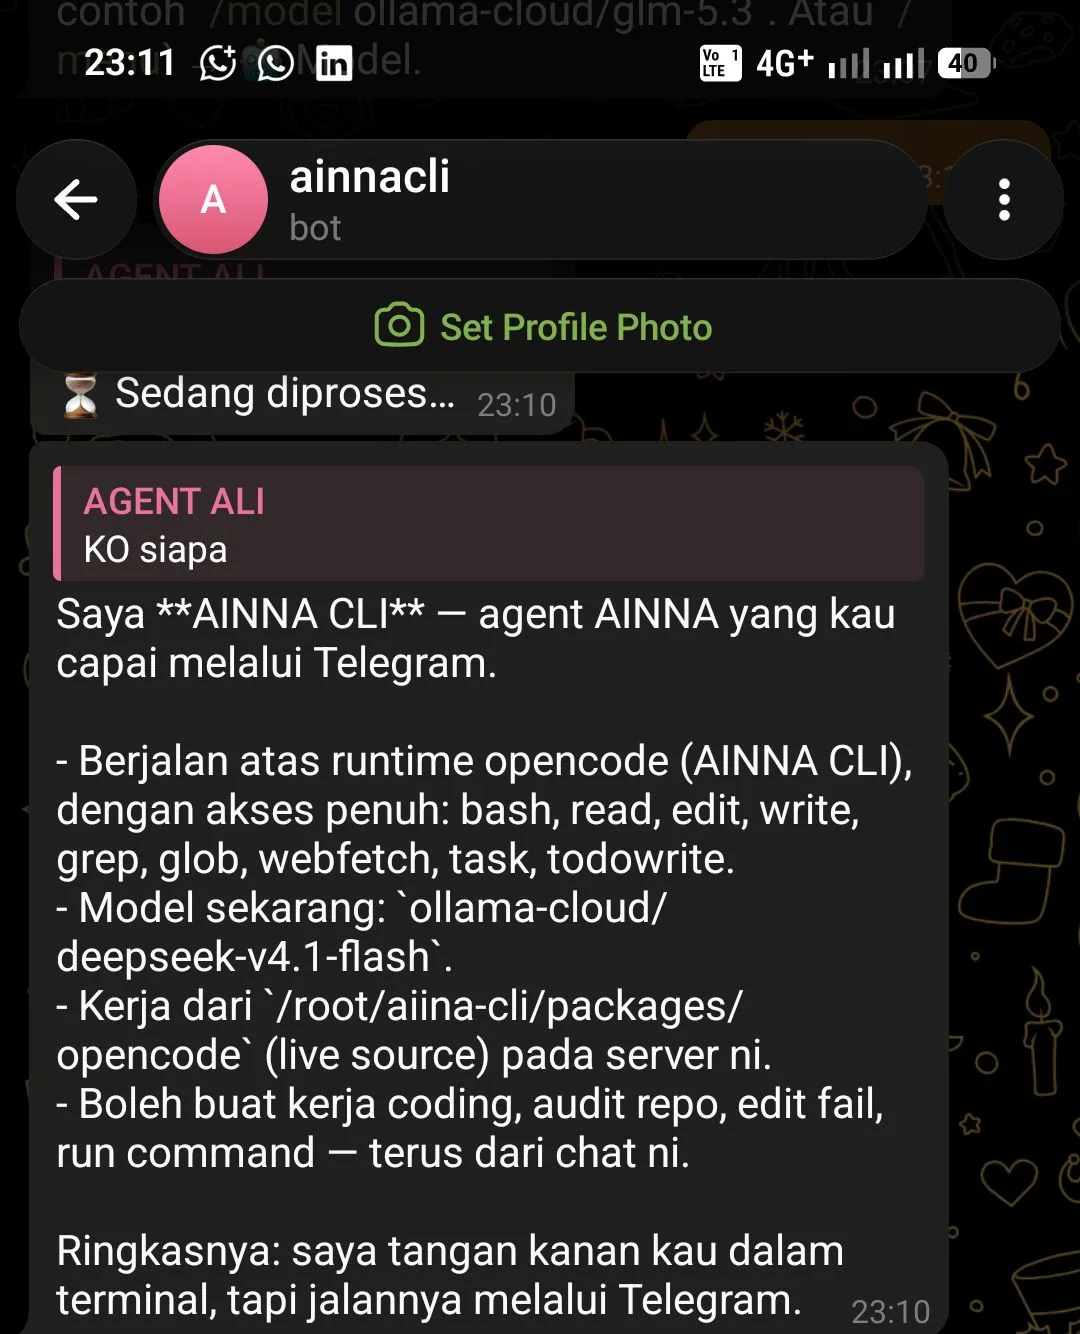
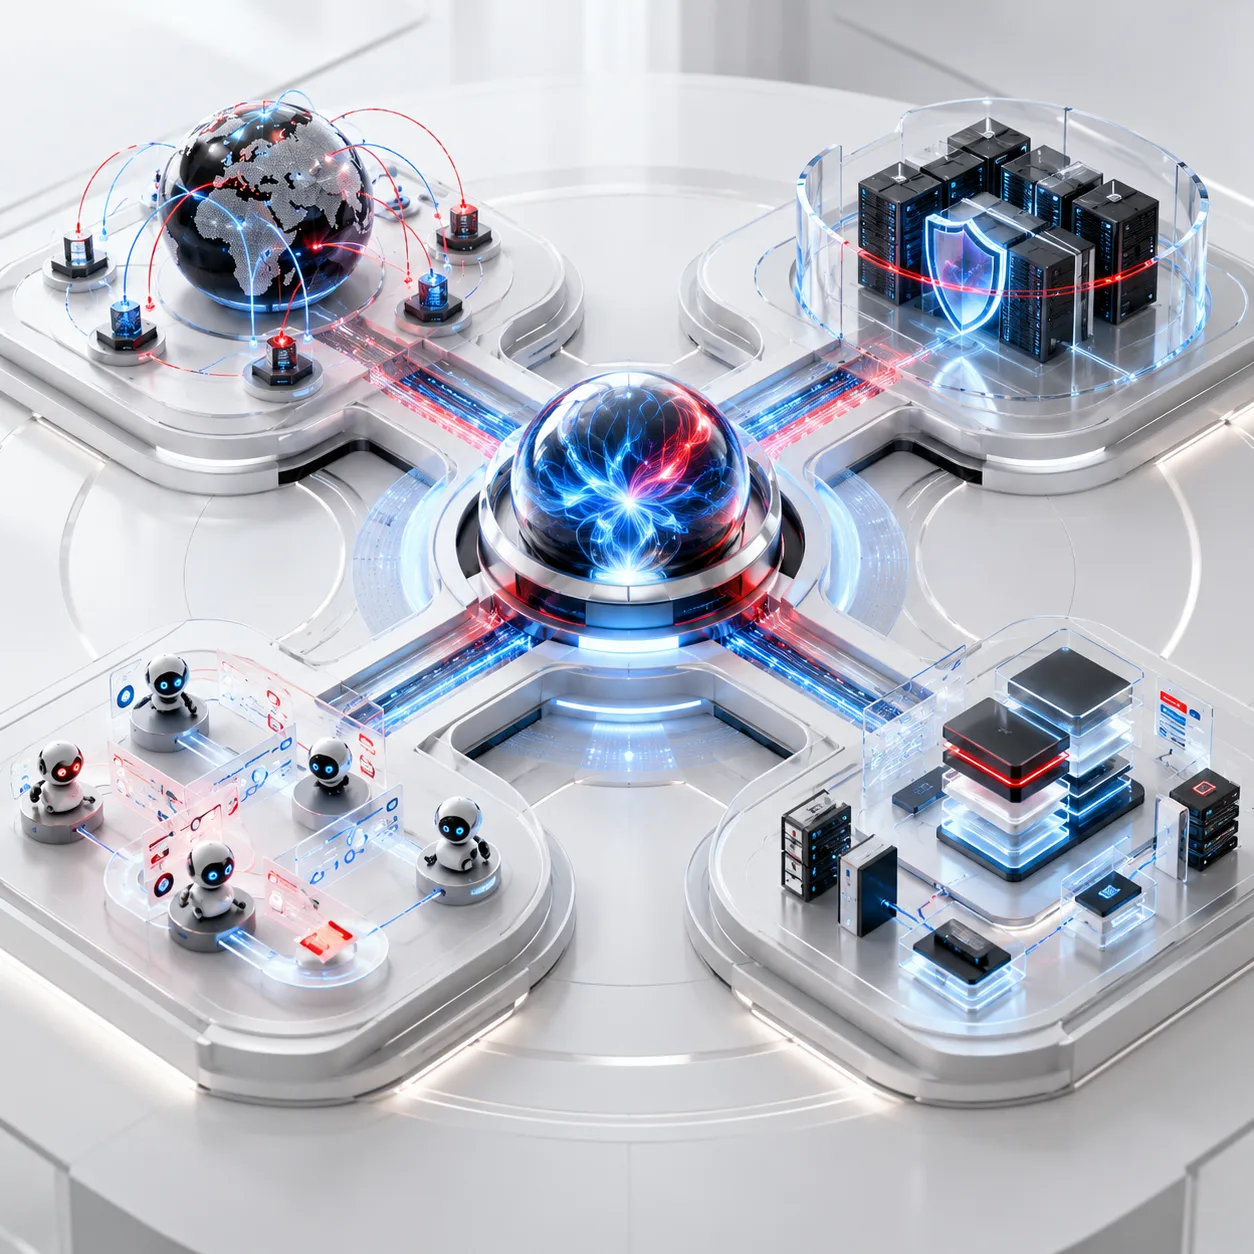
Instead of just shipping software, we're now embedding a 实时 AI agent inside the 系统 itself - running within defined 工作流, permission scopes, guardrails and kill-switch controls.
从 an engineering standpoint, the most interesting part is the level of acceptance.
A few years back, getting VM access inside certain organisations - even for a small, isolated application - could be an uphill fight.
今天, some are already open to letting a 实时 AI agent operate with sudoer privileges, and in tightly controlled cases, even full root access inside an isolated VM.
That is a significant shift.
It tells me the conversation has moved past whether AI is capable enough. The real questions are now about trust, control, security, and how safely an AI agent can operate inside real organisational infrastructure.
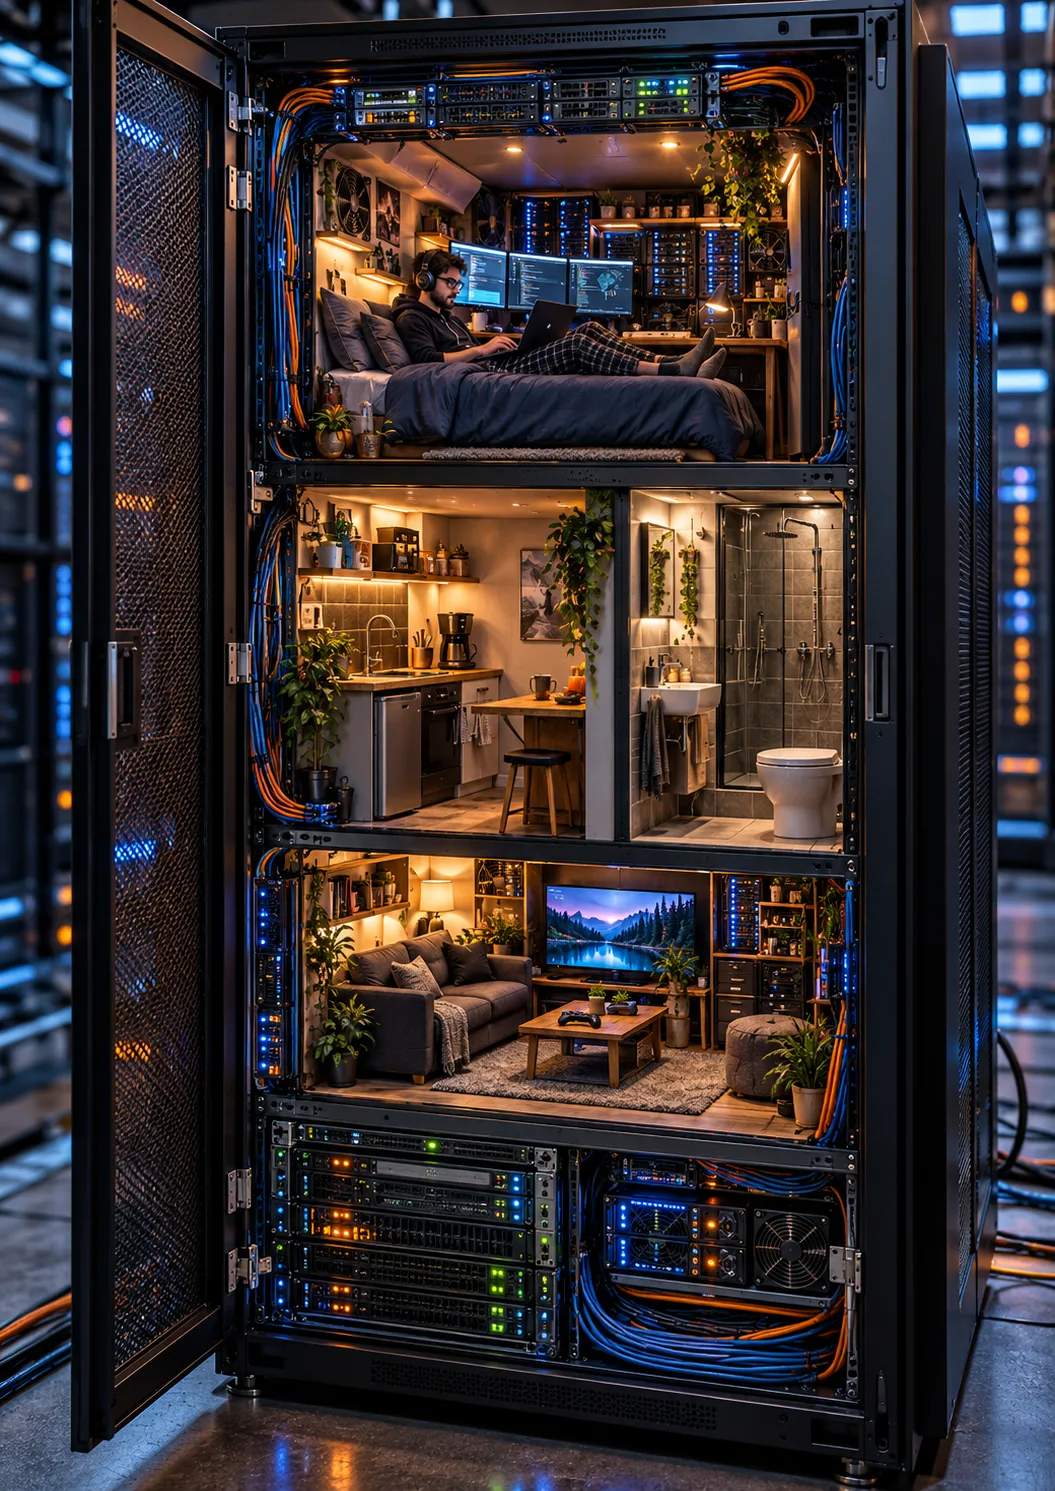
Once that trust is established, AI stops being just another application.
It becomes part of the operating layer.
Ultimately, our vision is to inject our own AI 智能体 and LLM intelligence layer into every client 系统, turning each deployment into an adaptive asset that grows in capability and value over time.
#AgentAI #AI基础设施 #企业版AI #AI自动化 #LLM #DigitalTransformation #AI工程













Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
我会把isolated application这一段分享给需要了解技术的同事。
Yesterday I spent the whole这个说法我要拿回去跟同事讨论。
如果有更多we're now embedding a 实时的数据和结果会更完整。
文章对从 an engineering standpoint提供了很好的起点,值得继续跟进。
关于kill-switch的实际落地部分最吸引我。
关于这部分的数字比我平时看到的大多数文章靠谱。