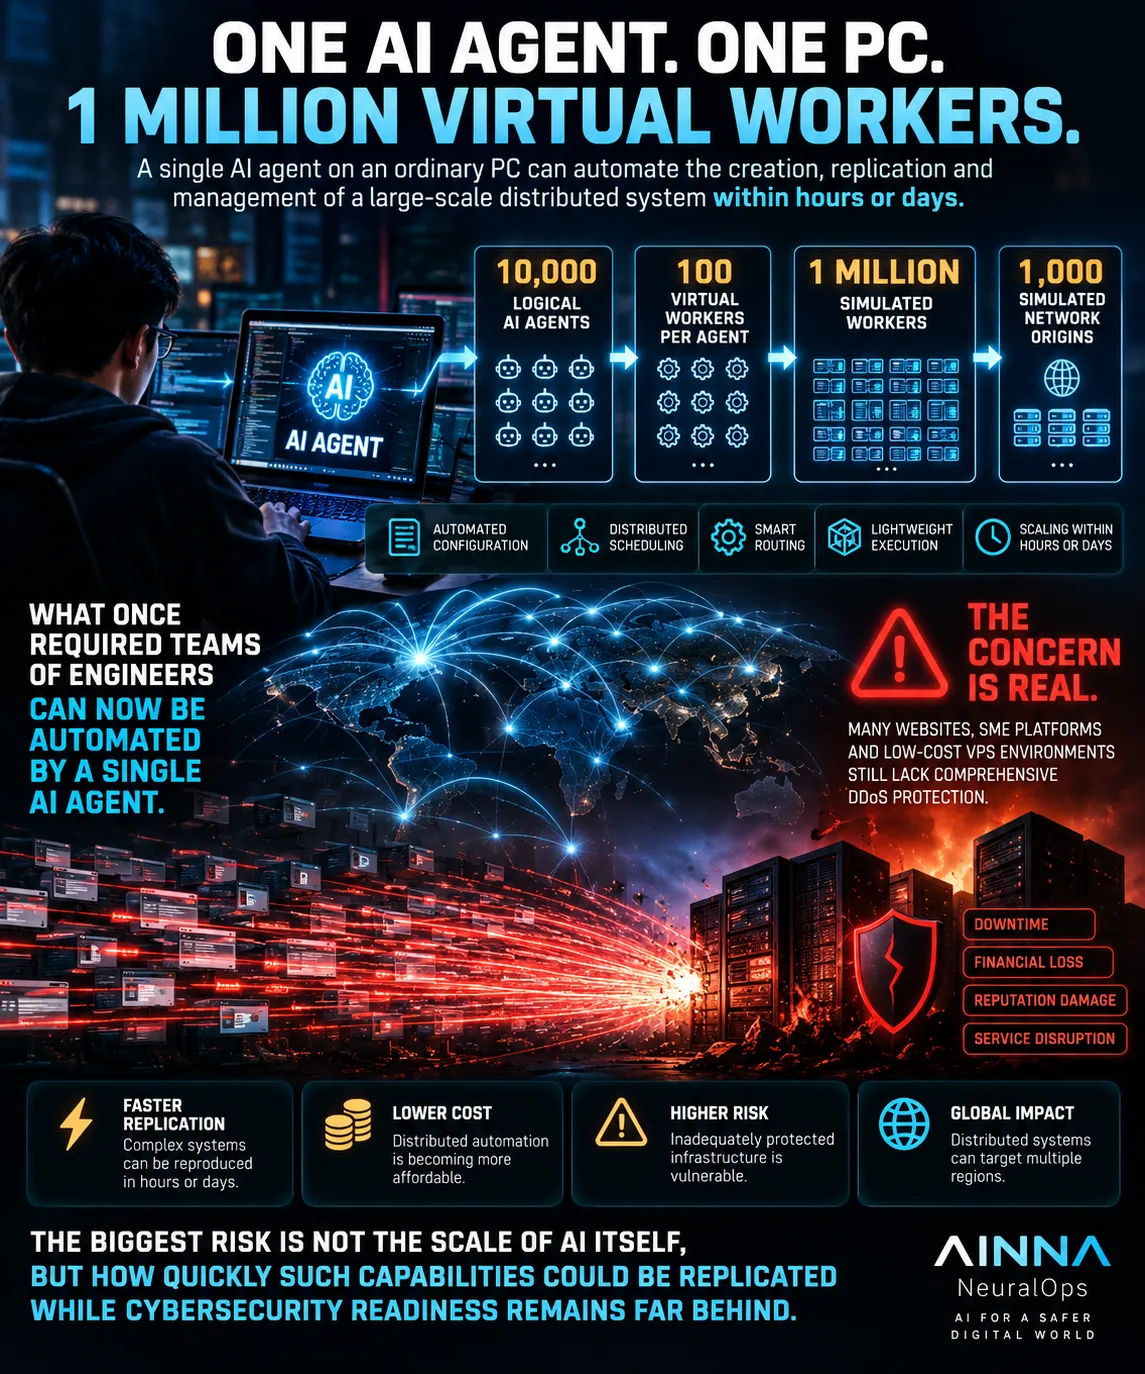
The cybersecurity issue I keep coming back to isn’t raw compute. It’s how fast an AI-driven control plane can replicate and scale distributed 系统 once the orchestration pattern is proven. Picture one agent on a commodity PC orchestrating 10,000 logical agents, each with 100 virtual workers-1 million simulated workers across 1,000 virtual network origins, with independent scheduling and task execution. That’s a 系统 设计 problem: identity, queues, routing, rate limits, logs, and cleanup.
With 小 语言 Models (SLMs), 智能路由, and lightweight execution stacks, I can automate a surprising amount of the architecture, configuration, and replication work. Some pieces still need engineering discipline-state management, backpressure, failure isolation-but the setup loop is compressing from weeks to 天数, and for narrow tasks to hours. Capability that used to require a dedicated platform team is now within reach of a small automation pipeline.
Now put on the security hat. Plenty of 中小企业 websites, self-hosted apps, and low-cost VPS deployments still run without serious DDoS protection. As distributed AI gets cheaper to stand up and easier to scale, underprotected infrastructure becomes a more attractive target surface. 模拟 workers are not the same as independent traffic sources-there are real constraints around egress, IP reputation, and network topology-but the speed and accessibility of distributed automation are already an emerging security problem.
The biggest risk isn’t AI’s scale on paper. It’s how quickly teams can replicate these capabilities while cybersecurity readiness, observability, and defensive controls stay far behind.
#AINNA #NeuralOps #AgenticAI #分配dAI #网络安全 #AI基础设施 #DDoS防护

Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
关于100的数字比我平时看到的大多数文章靠谱。
如果还有100的后续,我会继续读。
关于now put on the security的说明很完整,基础部分尤其清楚。
难得有人把that’s a 系统 设计 problem讲得这么直白。
看第二遍才注意到with 100 vir 100的细节。
这篇文章适合团队用来开始讨论underprotected infrastructure becomes。