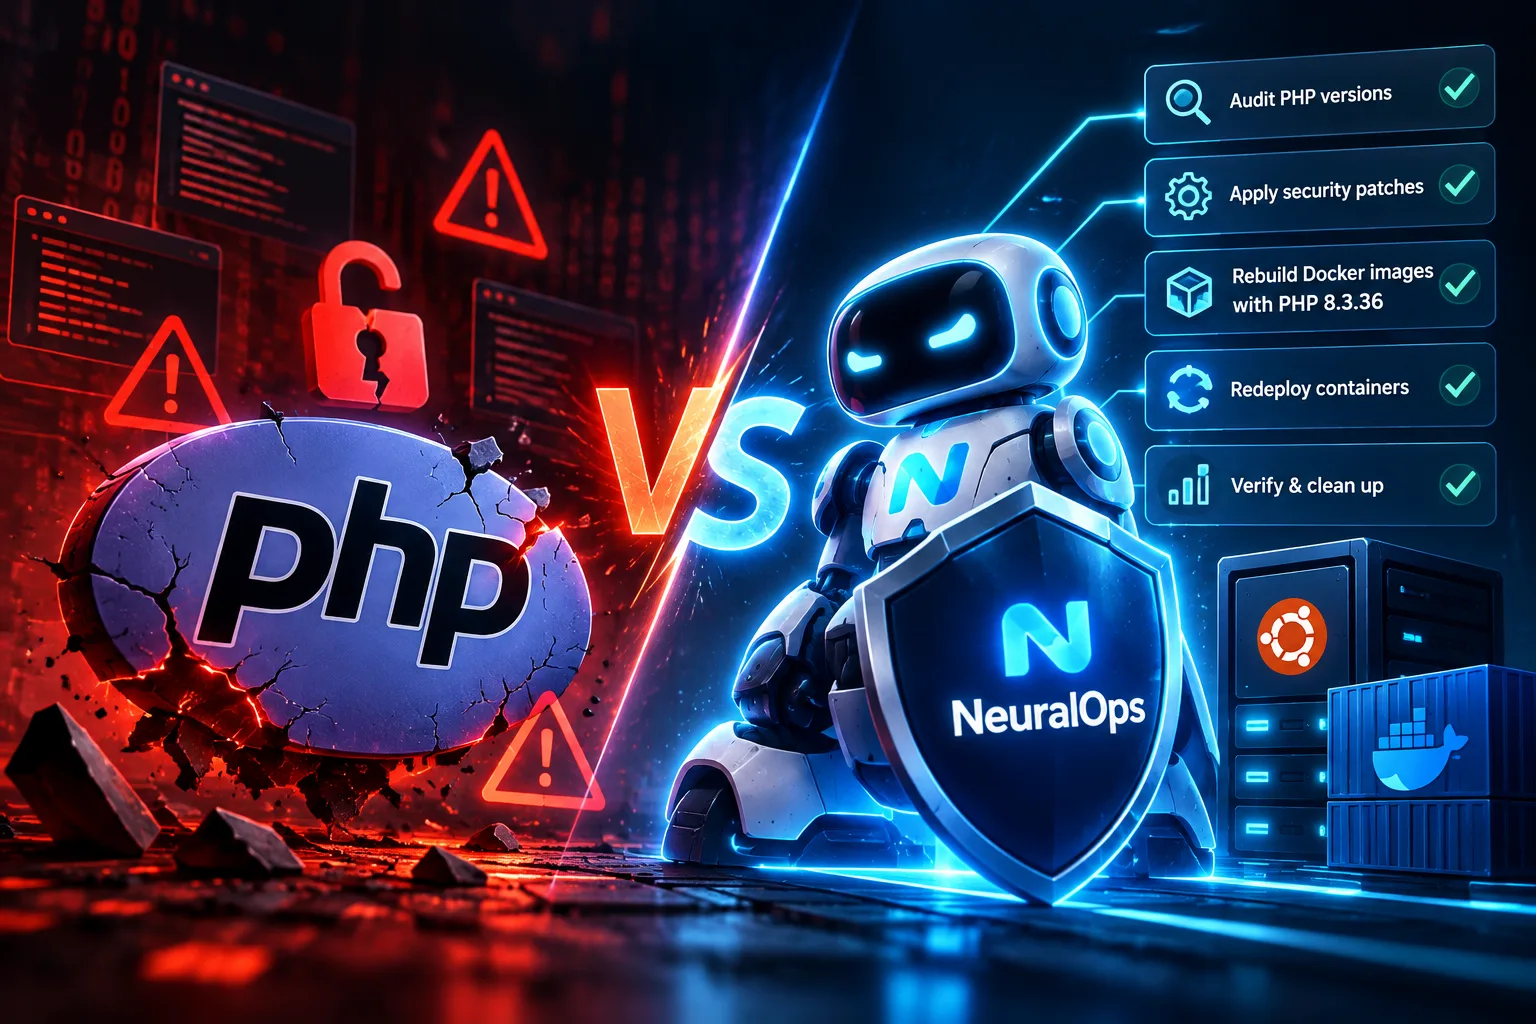
时间 the latest PHP security advisory landed, I didn't open a terminal and start typing. I scoped the fleet for our AI 智能体, and it worked the problem end to end: audit every server, fingerprint the running PHP versions, flag the vulnerable ones, apply the patches, then prove the stack still held up afterward.
Nobody hand-typed hundreds of Linux commands. We handed over intent in natural language, and the 代理 ran the execution chain - inventory, version checks, patch application, automated testing and security validation - with a human sitting at the approval 关卡 for every step that touched production.
That is the shift we are building at AINNA through AINNA NeuralOps. Getting a model to answer a question is the easy half. The hard half is wiring in tool access, guardrails, rollback paths and observability so an agent can act on 实时 系统 without becoming the next incident report.
从 asking AI to do something, to actually getting things done.
#AgenticAI #AINNA #NeuralOps #PHP #Cyber安全 #AI自动化


Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
如果可以继续说明automated testing and security validation的真实案例,我会想继续阅读。
这篇文章对从 asking AI的解释很清楚,实际操作的重点也很容易理解。
关于flag the vulnerable的例子很实用,适合团队继续讨论。
难得有人把getting a model to answer讲得这么直白。