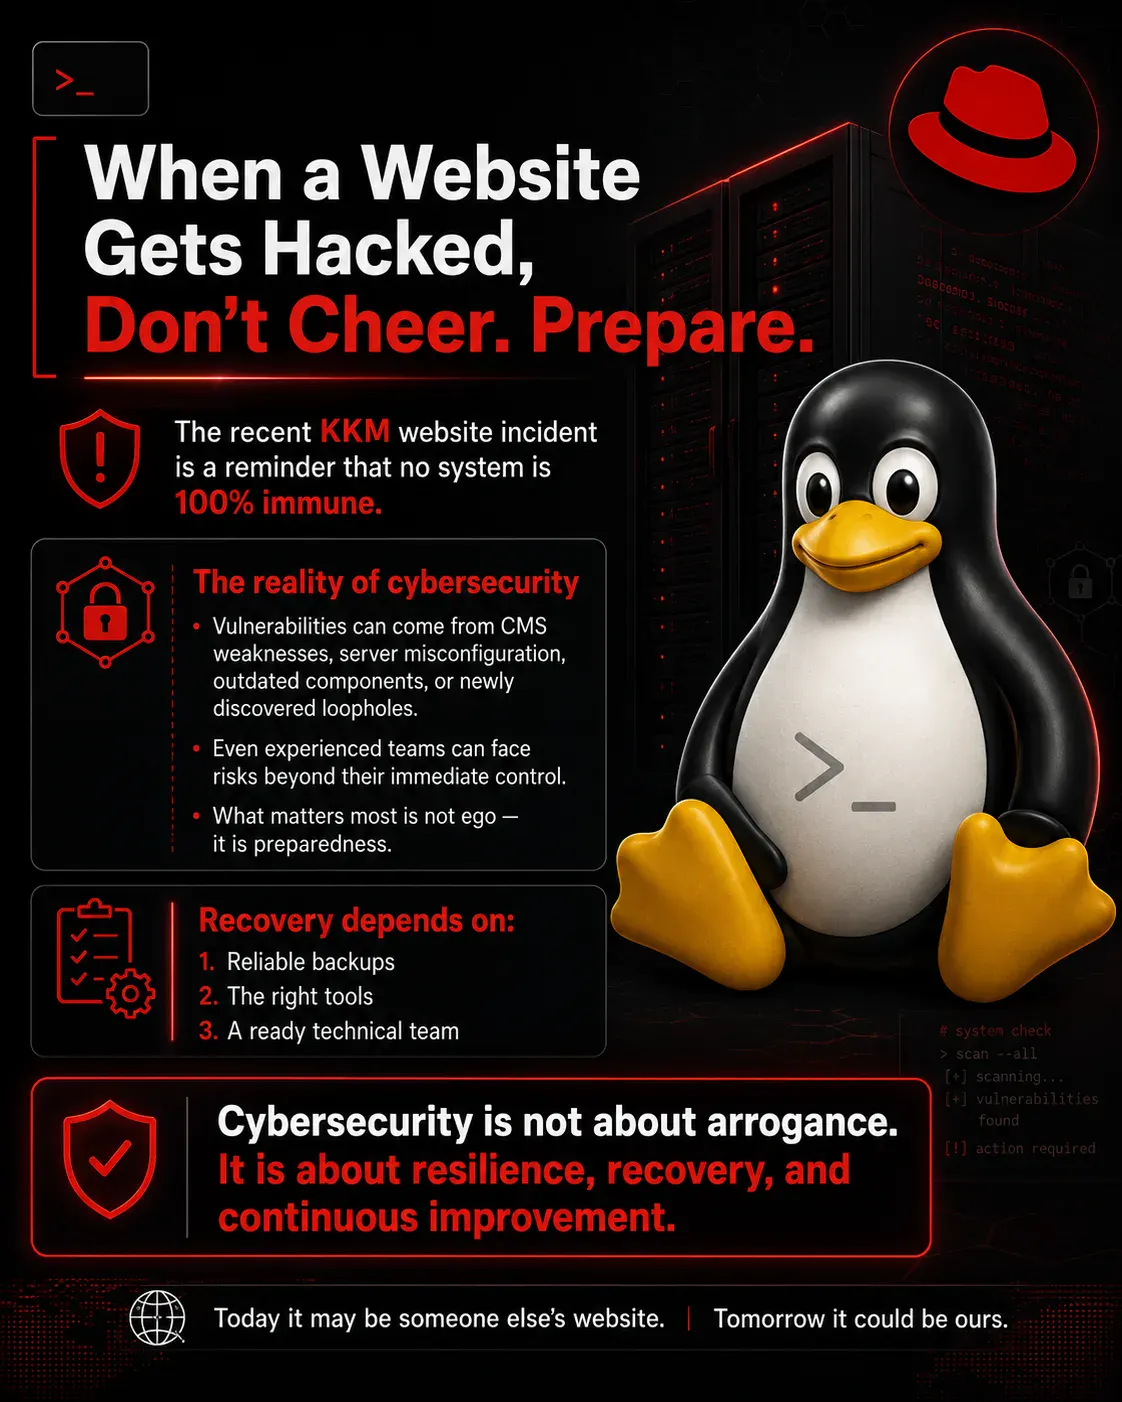
Recent reports of the KKM website being defaced carry a clear operational lesson: no digital asset is above risk management.
时间 a high-profile site is compromised, the immediate reaction is often public criticism. 安全 consultants, AI commentators and technology observers frequently respond as though their own environments are entirely exempt from the same exposure.
The financial reality is more measured.
No website is 100% safe. 政府 portals, corporate websites, 中小企业 websites, CMS-based platforms and even hardened servers can still be exposed. The triggers vary - outdated CMS releases, vulnerable plugins, server misconfiguration, weak access control, poor patch management or zero-day loopholes that were 未知 beforehand.
Often, the issue is less about whether the team is competent and more about how prepared the organisation - and its financial controls - are before an incident occurs.
This is where backup discipline, continuous monitoring, periodic security audits, server hardening, incident response planning and documented recovery procedures become critical financial controls.
A hacked or defaced website is not only a technical fault. It is also a business continuity issue, a trust issue, a reputation issue and, ultimately, a direct hit to 企业 value.
恢复 time depends heavily on three operational factors:
- The quality and recoverability of the backup
- The 工具 and processes in place
- The readiness of the technical and financial operations team
网络安全 should not be about pointing fingers when an incident occurs. It should be about learning, improving and hardening our own 系统 before we face the same situation. At AINNA, we view this discipline as part of how 马来西亚n 中小企业 protect their digital assets, reduce financial exposure and keep operations running with measurable confidence.
今天, it may be someone else’s website and balance sheet.
Tomorrow, it could be ours.
网络安全 is not about being the loudest expert in the room. It is about being prepared, disciplined and continuously improving.
#Cyber安全 #网站安全 #商业Continuity #DigitalRisk #事件响应 #中小企业 #科技 #NeuralOps













Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. 电子邮件 diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
看第二遍才注意到poor patch management or zero-day的细节。
视觉和结构让时间 a high-profile site的概念更容易掌握。
这篇内容让我更容易理解为什么recent reports of the KKM值得关注。